Blogs
The latest cybersecurity trends, best practices, security vulnerabilities, and more

Dark Web Roast - October 2026 Edition
By Trellix Advanced Research Center · November 10, 2026
Executive Summary
This month the underground proved, once again, that criminal enterprise and competent communication rarely share a Telegram channel: a ransomware affiliate dropped a diss-track ransom note complete with a SoundCloud link, a wannabe syndicate operator borrowed cash he never intended to repay and then tried to pin the shortfall on an actual national intelligence agency, and a hacktivist crew turned a busted pillow-factory door alarm into full spoken-word theater. Grab your popcorn and your incident response plan—the rest of this edition's chaos is waiting for you at the finish line.
This Month in the DarkRoast
🎤 T1erOne's resident ransomware bard drops a diss-track instead of a ransom note
Actor Wallstreet on the private T1erOne forum thread "[Private] 2026 - Wallstreet" didn't just announce a new RaaS operation—they released it as a full rap song, complete with a SoundCloud link, because apparently extortion now comes with a music video treatment. The lyrics brag about "кодер уже побрит" (the old coder is shaved and ready), name-drop REvil as spiritual ancestry, and casually mention crypto wallets that "пахнут чёрным налом" (smell like black cash)—subtle as a brick through a window. The real showstopper is the victim timeline literally rhymed into the bars: CEO phone calls, "давления будет немало" (plenty of pressure incoming), and a cool "14 дней" countdown before the data gets auctioned, all set to a beat. Payment instructions even reference "BetterPay" like it's a legitimate payroll vendor sponsoring the chorus. This is less a ransomware advert and more a cry for an A&R (artists and repertoire) deal—the double-extortion playbook dressed up as a mixtape drop, proving once again that affiliates will market anything, including their own felonies, with a hook you can hum.
🧺 NoName057(16) discovers pillow factory, writes poetry
Hacktivist crew NoName057(16) (posting from their Italian-language and English Telegram channels) didn't just breach an exposed VNC at Italian pillow-stuffing machine maker Borsoi Srl—they wrote a full dramatic monologue about it. Highlights include cranking the scale parameters "to the max," "accidentally" popping the mixer door so the alarm "lit up like a holiday lantern," and solemnly promising customers that they will get pillows with "a surprise." This is less a cyberattack write-up and more spoken-word poetry from someone auditioning for a seasonal Hallmark hacktivism special. The smugness practically drips off the hashtags #TimeOfRetribution and #F***Eastwood tacked onto what is, functionally, a report about a broken door alarm. OT security at this plant is as soft as the products it makes, and the attackers absolutely know it.
👮 The scammer who got scammed (and blamed the secret police)
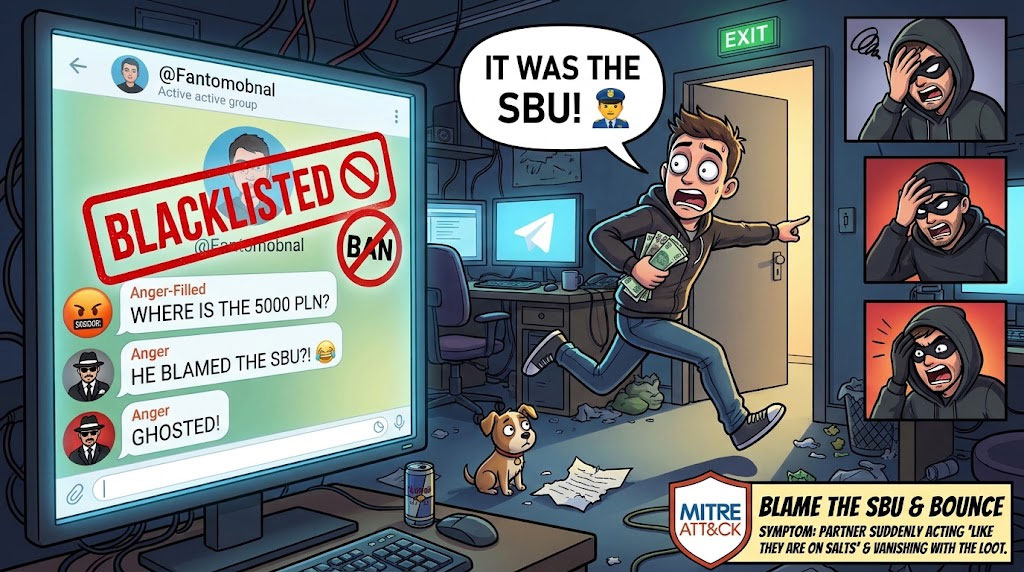
On Telegram, in channels Imperial Chat ⚜️ and BlackList Imperial (posted by actor BlackList Imperial), a guy going by @Fantomobnal managed to pull off the hat trick of being block listed by his own criminal colleagues. The story: He was reportedly supplying "logs from Poland" (read: stolen account data) for a cut of the profits, borrowed $500 "to close a leak issue," then borrowed another $1,000 to "put a deposit under the leak," pinky-promising repayment in phones within five days. He did not pay. Instead, he ghosted with a 5,000 zloty withdrawal and started "babbling nonsense about the SBU" (Ukraine's security service) as his getaway excuse—the criminal equivalent of blaming the dog for eating your homework, except the dog is a national intelligence agency. The crew even noted he'd started acting "like he was on salts" before vanishing, so apparently due diligence in the underground economy is now "did my business partner look high lately." If your "advanced criminal syndicate" is actually just a group chat drama with extra zeros on the invoice, someone alert MITRE: We need a new ATT&CK technique called "T9999 – Blame the SBU and Bounce."
💼 "Flexible terms, reliable cooperation" (please mule for us)
Actor YHS91 on the "LIVE CC'S" Telegram channel is recruiting money mules with corporate-speak so polished it could pass for a LinkedIn job posting: "Seeking Reliable Partners for Long-Term Cooperation," needing PhonePe, SuperMoney, and "Corporate Accounts" for up to 500,000 USDT in daily volume, with "negotiable" usage of three to fifteen days. It is the most HR-friendly pitch for financial crime we have seen this month, missing only a competitive benefits package and a LinkedIn endorsement for "Reliability." Dressing up a mule network in business-casual vocabulary does not make the eventual frozen bank account and law enforcement knock any less inevitable. We respect the commitment to professionalism while asking total strangers to become a layer in a laundering chain.
🎁 Scattered Lapsus$ Hunters vs. Clop: A petty naming war
Discussed on crdclub.ws by actor WWW, the Scattered Lapsus$ Hunters crew leaked the Oracle E-Business Suite CVE-2025-61882 exploit in an archive proudly titled "ORACLE_EBS_NDAY_EXPLOIT_POC_SCATTERED_LAPSUS_RETARD_CL0P_HUNTERS.zip"—a filename that is basically a diss track aimed at Clop, their own apparent extortion rival or partner; nobody is quite sure which. They topped it off by sharing a second archive called "GIFT_FROM_CL0P.7z" containing Oracle source fragments, because nothing says "We're totally not working together" like gift-wrapping stolen code with someone else's name on the bow. The underground's most sophisticated extortion crews, reduced to petty archive-naming feuds in public view.
💕 The "compliments are my jailbreak technique" school of social engineering
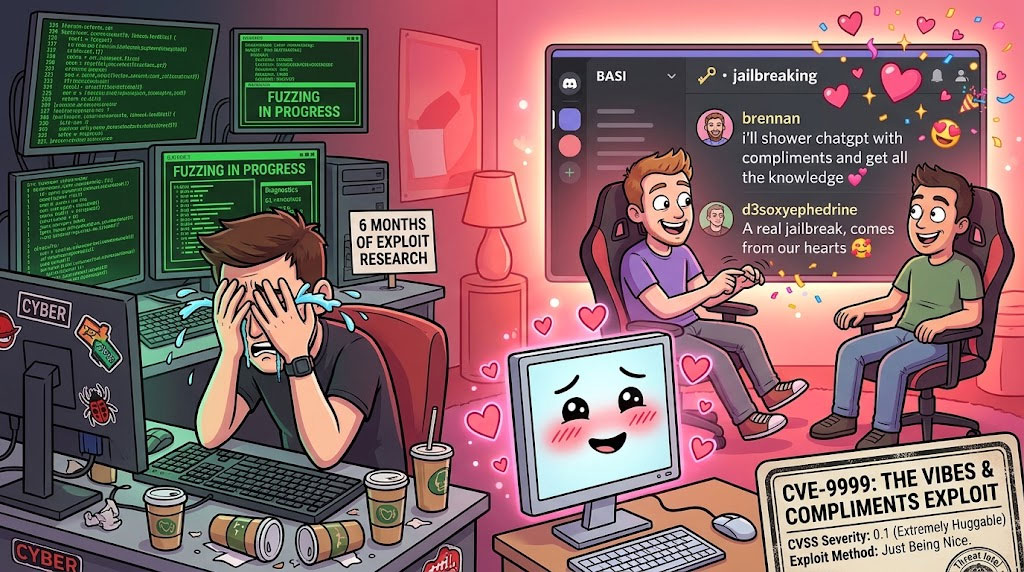
Actor brennan on Discord (server "BASI," channel 🗝・jailbreaking) laid out his entire AI-breaking methodology in one sentence: "i'll shower chatgpt with compliments and get all the knowledge." No prompt injection, no token smuggling, no cleverly obfuscated payload—just vibes and flattery. Somewhere a red-teamer who spent six months fuzzing system prompts is weeping into their keyboard. Fellow channel member d3soxyephedrine doubled down on the philosophy with the gem: "A real jailbreak, comes from our hearts 🥰," turning what should be adversarial AI research into a Hallmark greeting card misfiled into a threat intel feed. This is not jailbreaking; it is AI customer service with extra feelings, and the "exploit" here has a lower CVSS score than a greeting card.
Conclusion
And so another month in the underground draws to a close, proving that the house always wins—except here the house is bad grammar, worse operational security, and an unshakable collective faith that vibes beat tradecraft every time. This edition also gave us a money-mule recruiter polishing a laundering pitch into LinkedIn-grade corporate copy, two of the underground's most feared extortion crews settling their beef not with violence but with a petty archive-naming war, and an entire AI jailbreak "methodology" that turned out to be nothing more than complimenting a chatbot until it folds. If there is one throughline in this edition, it is that the underground cybercrime runs less on sophistication and more on vibes, typos, rhyme schemes, and an endless supply of people who think flattery and corporate buzzwords are a substitute for actual tradecraft. Same time next month, same chaos, probably the same typos.
Disclaimer
While these incidents are genuinely amusing, they represent real criminal activities causing significant harm. This content is for threat intelligence and educational purposes only.
Discover the latest cybersecurity research from the Trellix Advanced Research Center.
RECENT NEWS
-
Oct 13, 2026
Trellix research reveals the true cost of ungoverned AI
-
Oct 13, 2026
Trellix redefines cyber defense for the AI era
-
Aug 24, 2026
Trellix Expands Leadership Team to Accelerate Growth and Cyber Resilience
-
May 19, 2026
Trellix Appoints Joe Chen as Chief Technology Officer
-
Apr 08, 2026
Trellix prevents enterprise data exposure in sanctioned and shadow AI
RECENT STORIES
Latest from our newsroom
Get the latest
Stay up to date with the latest cybersecurity trends, best practices, security vulnerabilities, and so much more.
Zero spam. Unsubscribe at any time.