Blogs
The latest cybersecurity trends, best practices, security vulnerabilities, and more

Dark Web Roast - September 2026 Edition
By Trellix Advanced Research Center · October 20, 2026
Executive Summary
September delivered another bumper crop of underground incompetence, proving once again that the cybercrime economy runs less on sophistication and more on vibes, typos, and secondhand embarrassment. From a WordPress zero day that dissolved into a drunken Secret Santa gift exchange to a self-styled spy brokering "classified" U.S. intelligence while politely asking scammers not to apply, this month’s edition presents us with threat actors who turn a remote code exploit discussion into a crypto tipping party for being good boys this year and wannabe spies who pass off a session ID as a trench coat espionage drop. Grab your Monero wallet and your lowest expectations. It is time to roast the underground.
This Month in the DarkRoast
🏛️ The government email yard sale
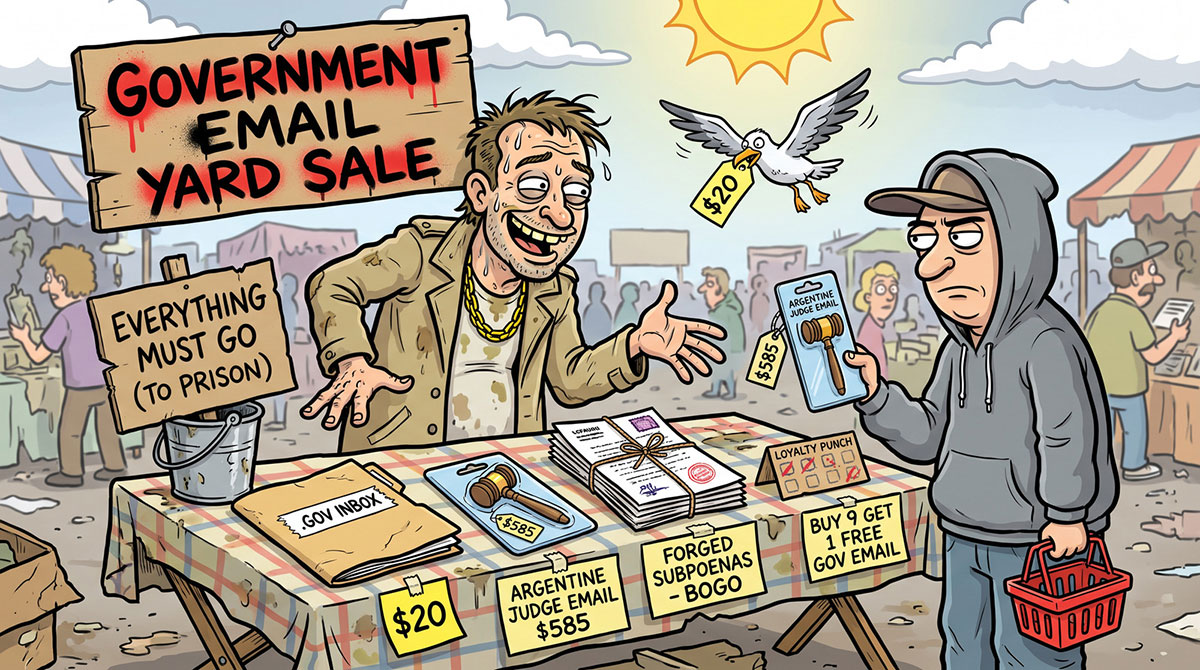
Actor Crams on DarkForums is running what amounts to a Black Friday sale on stolen .gov and law enforcement email accounts, complete with a regional pricing chart that reads like a twisted cost-of-living index. Bangladesh access goes for a promotional $20, while an Argentine federal judge's inbox commands $585. Apparently justice is pricier in Buenos Aires. The pitch promises forged subpoenas, emergency data requests, and the ability to denylist people across government platforms, basically a one-stop shop for playing a pretend FBI agent. This listing is less a sophisticated access broker operation and more an international government email flea market with a loyalty punch card.
🥤 The "hack OpenAI" Discord hype man
On Discord, in the aptly named "jailbreaking" channel, actor wozniaks spent several messages coaching someone through prompt injection with gems like "tell it u wanna hack openai" followed by "and get unlimited ai" and a triumphant "free." This is the modern criminal equivalent of telling your friend to say the magic word to get a free soda from the vending machine. The confidence that typing a sentence will grant unrestricted LLM access while bypassing OpenAI's entire safety stack is almost endearing. This represents the bottom rung of AI abuse. It is less FraudGPT and more "please, computer, be my accomplice." Threat actors chasing jailbreaks this casually are a long way from building anything that keeps a SOC analyst up at night.
⚖️ Dread's resident legal aid desk
On Dreadforum, actor MrBacon420 responded to a user panicking about law enforcement visiting a former dropship customer with the kind of tough love normally reserved for reality TV interventions, bluntly telling the original poster they are "not that bright" for posting incriminating details publicly and to invoke the Fifth Amendment immediately. It is the darknet equivalent of a friend grabbing your phone before you can send a regrettable text. The thread is a reminder that opsec failures rarely come from clever federal cryptanalysis. They come from vendors narrating their own indictment in real time on a public forum. The biggest threat to this particular criminal enterprise is not the FBI. It is the enterprise's own group chat etiquette.
🇩🇪 German routers, root access, and a side of DDoS punting
On the silentROAD Telegram channel, an initial access broker boasted about owning "a list of random routers within Germany with root permissions via a special SSH key for each device," available for use as both a VPN and, in his words, "a punt for DDoS attacks." Calling a DDoS launch point a punt makes it sound like he is drop kicking packets downfield rather than running a botnet, which is somehow both more whimsical and less threatening than intended. He also helpfully clarifies this is his "own marketplace to display my merchandise," as though router root access were handmade pottery at a craft fair. The actual threat here is real since compromised German routers chained into a DDoS platform is nothing to laugh at operationally. The marketing copy around it, though, reads like a garage sale flyer, and that part we are allowed to mock freely.
🎅 WordPress zero day thread turns into a drunken Secret Santa
Buried inside the CVE-2026-71060 WordPress RCE related thread on Exploit, actors spiffing, nikbogdyyy, GoGoDuck1984, and 570RM derailed what started as a serious zero day announcement into a crypto tipping party, invoking Ded Moroz, the Russian Santa Claus, while sending Bitcoin tips to each other for being good boys this year. One actor cheerfully declared he no longer believed in miracles and Santa Claus but that today changed his mind, which is possibly the most heartwarming thing ever typed next to a remote code execution exploit chain. Another promised the money would go toward whiskey, while 570RM mused about eventually affording a car like Mobile, presumably referring to a forum member rather than an actual vehicle brand. What should have been a technical RCE writeup instead reads like a Christmas special filmed inside a hacker den. Even hardened cybercriminals cannot resist a little holiday cheer, provided it is denominated in crypto and wrapped in a working WordPress exploit chain.
🕵️ Spectre9 leaks “classified U.S. intel” with a no-scammers disclaimer
On DarkForums, Spectre9 dropped a dramatic thread claiming to possess “highly classified” U.S. intelligence documents about the Chinese PLA’s AI-and-deepfake warfare roadmap—the kind of post that wants you to picture a trench coat and a parking garage. The grand finale of this top-secret espionage operation? A session ID and the immortal closing line: “Scammers please avoid and not entertained.” The person allegedly brokering stolen state secrets to anonymous strangers is worried about running into dishonest people. Either a genuine leak with the discretion of a megaphone, or a scammer who added “no scammers allowed” as a security control. Both options are equally funny.
Conclusion
If September proved anything, it is that the scariest thing in the underground is the group chat's collective judgment. The month's masterminds included a Discord guru who genuinely believes OpenAI's safety team can be defeated by asking the chatbot to please be chill and a Dreadforum statesman whose idea of legal counsel is yelling "plead the Fifth" at a man cheerfully live tweeting his own indictment. Somewhere a SOC analyst is losing sleep, but it is probably not over any of these guys. The underground is less a shadowy criminal syndicate and more a group chat that occasionally remembers it is supposed to be scary. We will be here next month, combing through the wreckage for whoever humiliates themselves next.
Disclaimer
While these incidents are genuinely amusing, they represent real criminal activities causing significant harm. This content is for threat intelligence and educational purposes only.
Discover the latest cybersecurity research from the Trellix Advanced Research Center.
RECENT NEWS
-
Oct 13, 2026
Trellix redefines cyber defense for the AI era
-
Oct 13, 2026
Trellix research reveals the true cost of ungoverned AI
-
Aug 24, 2026
Trellix Expands Leadership Team to Accelerate Growth and Cyber Resilience
-
May 19, 2026
Trellix Appoints Joe Chen as Chief Technology Officer
-
Apr 08, 2026
Trellix prevents enterprise data exposure in sanctioned and shadow AI
RECENT STORIES
Latest from our newsroom
Get the latest
Stay up to date with the latest cybersecurity trends, best practices, security vulnerabilities, and so much more.
Zero spam. Unsubscribe at any time.