Blogs
The latest cybersecurity trends, best practices, security vulnerabilities, and more

What Happens in Private Cloud, Stays in Private Cloud
By Shristi Sharma and Faisal Pias, Sr. Partner Solutions Architect, AWS · November 19, 2026
Secure AI with AI, without your data leaving AWS
If your business runs on Amazon Web Services (AWS), your AI runs there too. Your models sit on Amazon Bedrock. Your autonomous agents run on Amazon Bedrock AgentCore. Your sensitive data lives in Amazon S3, and your workloads in a virtual private cloud (VPC). That is also where your security problem now lives, and it comes in two parts. In order to keep your data safe, you have to secure the AI you are building, including: the data it touches, the agents, the tool calls. You also have to secure with AI, because human-scale security operations can no longer keep pace with machine-speed attacks.
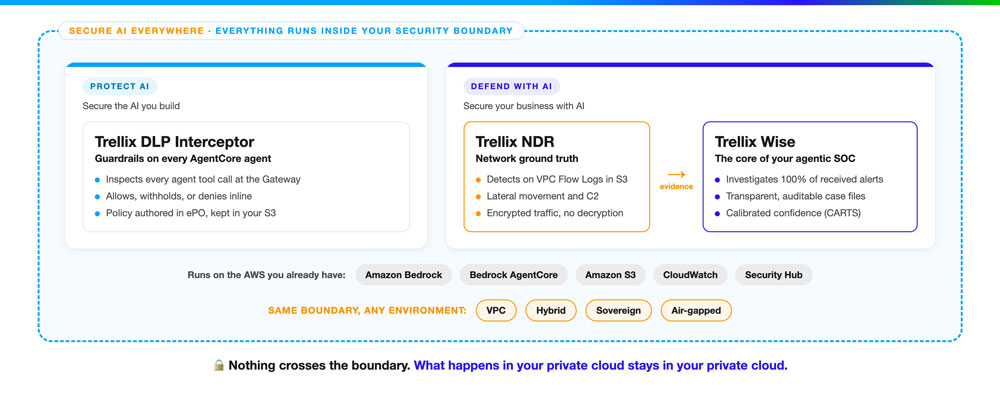
Trellix solutions built on AWS address both sides of thes AI security challenge—protecting AI environments and using AI to strengthen cyber defense—in the same place your business already runs. Together, Trellix and AWS deliver this approach through three foundational pillars (Figure 1).
- Protect AI: Guard the data, agents, models, and tool calls behind the AI you build.
- Defend with AI: Apply AI to security operations centers (SOC), backed by evidence from your own network, to accelerate threat detection, investigation, and response.
- Secure AI Everywhere: Extend security and governance across the entire AI ecosystem without compromising data sovereignty or control. Every piece runs inside your own security boundary, so what happens in your private cloud stays in your private cloud. You keep the data control your regulators expect, and you still get the latest AI. No compromise on data control.
Protect AI: How do you secure the agents you build on Amazon Bedrock AgentCore?
Every autonomous agent you stand up on Amazon Bedrock AgentCore opens a new attack surface. Agents query corporate databases, execute Model Context Protocol (MCP) tool calls, and generate automated responses. Attackers know it. They use prompt injection, indirect context poisoning, and privilege escalation to coax an agent into running an unauthorized query, pulling a restricted file, or quietly exfiltrating intellectual property.
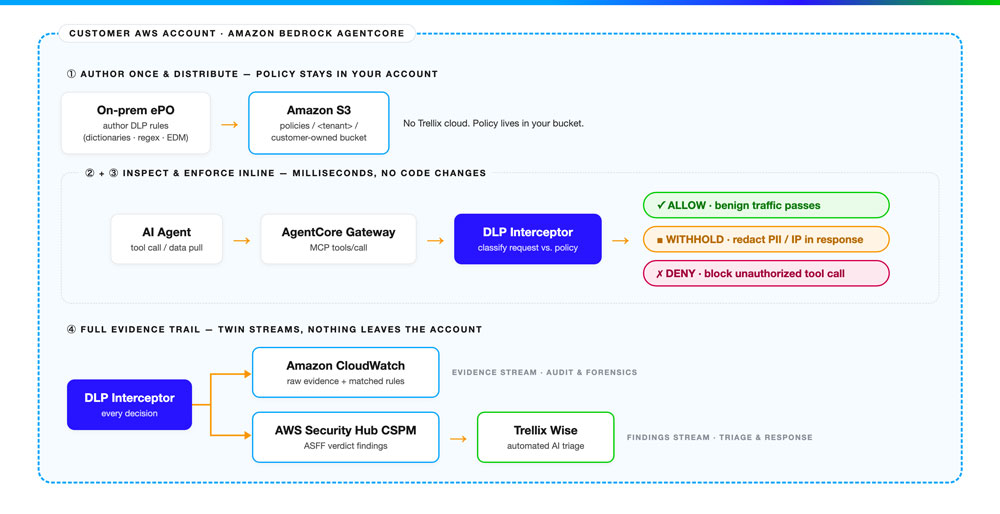
Trellix Data Loss Prevention (DLP) closes that gap. A containerized Trellix DLP Interceptor for AgentCore attaches directly to every AgentCore Gateway API endpoint. Designed to minimize added latency, there are no application code changes. Everything runs inside your AWS account, so data never leaves your environment (Figure 2):
- Author once, in the console you already use. Security teams write DLP rules in Trellix ePolicy Orchestrator (ePO) with the same dictionaries, regular expressions, and fingerprints they use everywhere else, then point them at the "AI agents" enforcement destination.
- Policy stays in your account. Rules are distributed to a customer-owned S3 bucket.
- Enforce inline, in milliseconds. When an agent makes a tool call or pulls data, the Trellix DLP Interceptor checks the request against your local policy. It denies the call (say, a destructive database operation), withholds sensitive content (PII, payment data, or proprietary IP redacted before it reaches the model's response), or allows benign traffic to pass untouched.
Evidence streams to Amazon CloudWatch. Verdict findings in ASFF format flow to AWS Security Hub CSPM, then on to your SIEM and to Trellix Wise for Private Cloud for automated triage.
Already built customer-facing agents on AWS? This is how you put real guardrails around them.
Defend with AI: How does Trellix Wise for Private Cloud become the core of your agentic SOC?
Attacks now move faster than any human-scale SOC can triage. Trellix Wise for Private Cloud is the core of your agentic SOC and keeps up with machine-speed attacks. Deployed natively inside your AWS VPC, Trellix Wise for Private Cloud investigates 100% of received alerts, produces verdicts informed by business context, and recommends a response (or executes one, within the limits you set). All model execution, retrieval, and reasoning run on your own instance. Your telemetry stays home.
Most AI security hands you a black box. Every Trellix Wise for Private Cloud investigation instead produces a transparent case file, a fully auditable record you can trace line by line back to its source evidence.
How can you trust Trellix Wise for Private Cloud? Every Trellix Wise for Private Cloud verdict carries a calibrated confidence rating that analysts can read but cannot inflate. The number is a weighted sum of independent signals: situational awareness, behavioral deviation, business context, history, and policy alignment. It follows the Open Secure AI Alliance-aligned CARTS Framework (Confidence, Auditability, Reversibility, Trust, Safety). When sources disagree, the score is penalized rather than averaged. When evidence is missing, Trellix Wise for Private Cloud records "No Reputation Available" rather than inventing a verdict. A regulated SOC needs exactly that kind of honesty. (For the full confidence model, see this white paper on the CARTS Framework.)
Who stays in control of the automation? You do. You decide what level of autonomy Trellix Wise for Private Cloud has. Low-risk, high-volume triage like enrichment, reputation lookups, and noise suppression can run fully automated. Higher-impact actions such as host isolation, account disablement, and firewall blocks require one-click analyst confirmation. Mission-critical changes stay manual. A permanent override lets SOC directors lock any action to human sign-off, and a single platform-wide emergency stop halts every in-flight command across your connected controls in seconds.
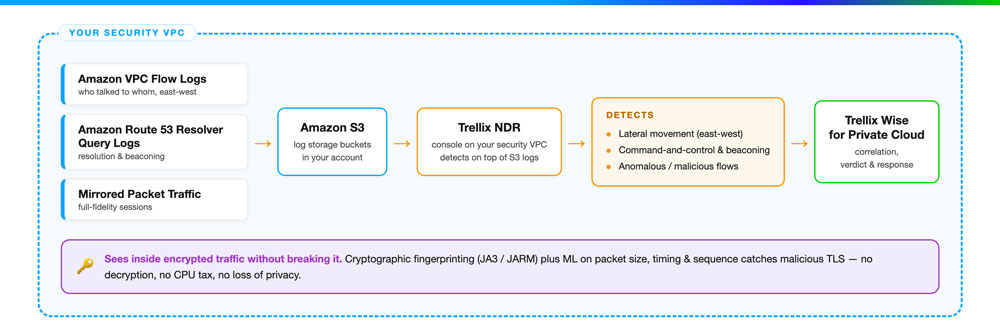
Where does Trellix Wise for Private Cloud get its evidence? From the security stack you already run. Trellix Wise for Private Cloud is vendor agnostic. It connects to your existing SIEM, endpoint, identity, and cloud tools and queries their data in place, so there is nothing to rip out and replace. What most stacks lack is ground truth from the network. AWS provides rich network telemetry, such as Amazon VPC Flow Logs, Amazon Route 53 Resolver query logs, and Amazon VPC Traffic Mirroring. Trellix NDR builds on that telemetry to detect lateral movement and other east-west activity, and feeds those findings into Trellix Wise for Private Cloud as evidence.
Trellix NDR is fully integrated with Trellix Wise for Private Cloud and can optionally integrate with Amazon Bedrock. Trellix NDR uses machine learning, behavioral analytics, and Trellix Wise for Private Cloud to identify anomalies, lateral movement in and out of your cloud instance, and command-and-control beaconing. It continuously ingests Amazon VPC Flow Logs, Amazon Route 53 Resolver query logs, mirrored packet traffic, and optional Infoblox telemetry into local Amazon S3 storage buckets.
Unlike passive network monitors that merely emit alert logs, Trellix NDR offers capabilities that merge traditional intrusion detection and prevention system (IDPS) active blocking with AI-driven behavioral analytics. Encrypted traffic is no blind spot either. Using cryptographic fingerprinting (JA3/JARM) and machine-learning analysis of packet size, timing, and sequence, Trellix NDR catches malicious TLS sessions without breaking encryption and without the CPU cost of decryption.
The result is a SOC that keeps pace with machine-speed attacks without sacrificing human oversight. Trellix Wise for Private Cloud does the investigative heavy lifting on every alert, and your analysts spend their time on the decisions that genuinely need a human.
Secure AI everywhere: How do you keep all of this inside your own boundary?
Everything described in this blog post runs inside your AWS account. The Trellix DLP Interceptor enforces policy from your own S3 bucket. Trellix NDR reads logs that never leave your storage. Trellix Wise for Private Cloud reasons on your own instance. None of it asks you to ship sensitive data to someone else's cloud.
Because Trellix Wise for Private Cloud and Trellix NDR run where your data already lives, you secure it the same way wherever you operate: VPC, hybrid, sovereign cloud, or fully air-gapped. Trellix Wise for Private Cloud runs in a two-way connected mode, a one-way restricted mode that disables all outbound telemetry, or a fully offline mode that takes cryptographically signed updates on physical media for classified networks.
Underneath, Trellix Wise for Private Cloud ships as a hardened, immutable image built on FIPS 140-3 cryptographic modules, with a Common Criteria NDcPP compliance mode, CAC/PIV authentication, Kubernetes hardening aligned toward DISA STIG, and identity controls aligned to NIST 800-53.
What will it cost you during an incident? Nothing extra. Trellix Wise for Private Cloud is licensed at a flat fee based on the compute you allocate, not on alert volume, so there are no per-alert charges or overage fees when an incident spikes your alert count. It queries your existing data in place with federated queries, so there is no second data lake and no ingestion tax. Your investigation, hunting, and remediation agents can work every alert you send them, around the clock. You scale with the infrastructure you provision, not with how many threats you face.
Why AWS and Trellix, together?
AWS gives enterprises the scalable cloud, data, and AI foundation they need to innovate. Trellix brings the security intelligence, data protection, and detection and response that make that AI safe to run. Put them together and you can protect AI, defend with AI, and secure AI everywhere, across cloud, hybrid, sovereign, and air-gapped environments, with full data control, explainability, governance, and predictable economics.
As customers move from experimenting with generative AI to running agents in production, the question we hear most is how to keep control of their data while moving fast. AWS provides a broad set of AI, data, and security services so customers can design security into their AI workloads from the start. Trellix extends that foundation with data protection and detection and response that run within the customer's own AWS environment and integrate with the AWS-native telemetry and security services they already use. With Trellix's experience protecting enterprise and highly regulated environments, security teams can adopt agentic AI with confidence, without changing the governance model they already trust.
Build on AWS and extend your security with Trellix. What happens in your private cloud should stay in your private cloud.
Want to see this ecosystem live? Visit us at Booth #1830 at AWS re:Invent.
Can't make it? Find Trellix Wise for Private Cloud on AWS Marketplace and request a demo tailored to your environment.
RECENT NEWS
-
Oct 13, 2026
Trellix redefines cyber defense for the AI era
-
Oct 13, 2026
Trellix research reveals the true cost of ungoverned AI
-
Aug 24, 2026
Trellix Expands Leadership Team to Accelerate Growth and Cyber Resilience
-
May 19, 2026
Trellix Appoints Joe Chen as Chief Technology Officer
-
Apr 08, 2026
Trellix prevents enterprise data exposure in sanctioned and shadow AI
RECENT STORIES
Latest from our newsroom
Get the latest
Stay up to date with the latest cybersecurity trends, best practices, security vulnerabilities, and so much more.
Zero spam. Unsubscribe at any time.